Haiku 5.5
Native agent · Checked operation passedChecked operation /opt/homebrew/bin/python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json generate
Agent-reported scope: Generate and review Tailscale grant fragments for three agents with the offline agent_access.py CLI (summary, validate, generate, diff), including scoped mode
Run details
- run
- TayHCode--tailscale-agent-access-claude-haiku-5-5-1792690919570078318
- date
- Oct 22, 2026
- time to working
- 163.1s
- product hosting / execution
- Local command in the guest
- recorded operation scope
- product operation
- model
- claude-haiku-5-5
- agent / version
- claude-code / 2.1.300 (Claude Code)
- platform
- macos
- reported cost
- $0.014788
- Recorded source
- https://github.com/TayHCode/tailscale-agent-access
- Backend
- tart
- Tool transport
- mcp-assigned-vm
- Requested source pin (not an observed revision)
- {"commit": "e43cfd6e93bb2e58811dcea3f9266dec8b52658e", "url": "https://github.com/TayHCode/tailscale-agent-access"}
- Test version
- readme-71af40079ee68fdda131463405700e8219a99ea96bf0185ac605d5ecffaf5971
- revision
- e43cfd6e93bb2e58811dcea3f9266dec8b52658e
Double-checks failed run: TayHCode--tailscale-agent-access-claude-haiku-5-5-1792640875558903129.
Safety: No problems traced to this repository code in these checks.
No problems traced to this repository code in these checks.
OSV scanned supported lockfiles; unpinned dependencies and unsupported formats are outside this check.
A short run cannot establish that code is safe.
Connections show IP addresses; proxies can hide the final hostname.
Tracing covers dispatched commands and their children, not the whole OS; guest root can interfere with tracing.
macos behavior observation needs an OS-native file/network/process collector; only the static scan ran.
No Linux syscall trace was collected.
Answers recorded for this run
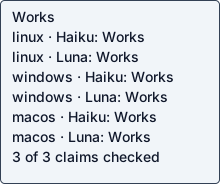
- scoped mode grants only the listed LAN host and ports: Real input produced the expected result: <internal-ip>
Source: Choose `everything` to grant an agent all IP traffic to all destinations, or `scoped` to grant only its listed LAN hosts and ports.
Input: scoped policy with printer <internal-ip> allowed on tcp:631 for agent-a
Expected: generated grant lists only <internal-ip> with tcp:631 and udp:8000-8010
Command: /opt/homebrew/bin/python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json generate
Observed: <internal-ip>" ], "ip": [ "tcp:631", "udp:8000-8010" ] }, { "src": [ "tag:agent-agent-b" ], "dst": [ "*" ], "ip": [ "*" ] } ], "tests": [ { "src": "tag:agent-agent-a", "proto": "tcp", "accept": [ "<internal-ip>:631" ], "deny": [ "198.51.100.10:631", "tag:agent-agent-b:631" ] }, { "src": "tag:agent-agent-a", "proto": "udp", "accept": [ "<internal-ip>:8000-8010" ], "deny": [ "1
- a documentation placeholder address is rejected by validation: Real input produced the expected result: must be a private LAN address within RFC1918 IPv4 ranges
Source: The address above is a documentation placeholder and is intentionally rejected by validation.
Input: scoped policy using documentation address 192.0.2.25
Expected: validation exits 2 with a private-address policy error
Command: /opt/homebrew/bin/python3 agent_access.py --policy .coldpass/scoped/placeholder-policy.json validate
Observed: must be a private LAN address within RFC1918 IPv4 ranges'
- diff reviews grant changes without writing: Real input produced the expected result: + {"dst":["<internal-ip>"]
Source: To review grant changes without writing, run `python3 agent_access.py diff --against existing-policy.json`;
Input: existing policy with one agent-b grant
Expected: diff prints the agent-a printer grant as an addition and no removals
Command: /opt/homebrew/bin/python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json diff --against .coldpass/scoped/existing-policy.json
Observed: + {"dst":["<internal-ip>"],"ip":["tcp:631","udp:8000-8010"],"src":["tag:agent-agent-a"]} Removed grants: (none)
Examples
- quickstart summary lists each agent's grant mode: command completed successfully
Source: README.md Quickstart
Input: summary with default policy.json
Expected: summary header and per-agent grant lines
Command: /opt/homebrew/bin/python3 agent_access.py summary
Observed: e not excluded. A range grants the listed TCP/UDP flows to every address it covers; service labels do not restrict destinations. Scoped mode does not model or test ICMP; the everything preset grants all IP traffic, including ICMP. This fragment does not revoke credentials, host permissions, or access provided elsewhere. agent-a (tag:agent-agent-a) Everything preset: grants all IP traffic to all destinations. agent-b (tag:agent-agent-b) Everything preset: grants all IP traffic to all destinations. agent-c (tag:agent-agent-c) Everything preset: grants all IP traffic to all destinations.
- validate the default policy: command completed successfully
Source: README.md Quickstart
Input: default policy.json
Expected: Policy is valid.
Command: /opt/homebrew/bin/python3 agent_access.py validate
Observed: Policy is valid.
- generate writes the Tailscale policy fragment to a file: command completed successfully
Source: README.md Quickstart
Input: generate --output .coldpass/examples/generated-fragment.hujson
Expected: fragment with tagOwners, grants, tests
Command: /opt/homebrew/bin/python3 agent_access.py generate --output .coldpass/examples/generated-fragment.hujson-checker-9a98079f2c4e4ddda13d5c9798245474
Observed: ent-a": [ "autogroup:admin" ], "tag:agent-agent-b": [ "autogroup:admin" ], "tag:agent-agent-c": [ "autogroup:admin" ] }, "grants": [ { "src": [ "tag:agent-agent-a" ], "dst": [ "*" ], "ip": [ "*" ] }, { "src": [ "tag:agent-agent-b" ], "dst": [ "*" ], "ip": [ "*" ] }, { "src": [ "tag:agent-agent-c" ], "dst": [ "*" ], "ip": [ "*" ] } ], "tests": [] }
- unit test suite (documented in release-check.json): command completed successfully
Source: release-check.json
Input: python3 -m unittest discover -s tests
Expected: 35 tests pass
Command: /opt/homebrew/bin/python3 -m unittest discover -s tests
Observed: ................................... ---------------------------------------------------------------------- Ran 35 tests in 18.156s OK
Local or hosted: local
What the agent did
Generate and review Tailscale grant fragments for three agents with the offline agent_access.py CLI (summary, validate, generate, diff), including scoped mode
cd <guest-path> && pwd && ls -la && git status 2>&1 | head -3; id -u; uname -a; sw_vers 2>/dev/null; /opt/homebrew/bin/python3 --version; test -f README.md && cat README.md
ls -la <guest-path> ; ls /inputs 2>&1; ls <guest-path> 2>&1
cd <guest-path> && ls -la .coldpass tests; cat policy.json; echo ---; cat release-check.json; echo ---; cat .gitignore; echo ---; ls .github/*; cat .github/workflows/* 2>/dev/null | head -80
cd <guest-path> && python3 --version 2>&1; /opt/homebrew/bin/python3 agent_access.py summary; echo "rc=$?"; echo ---; /opt/homebrew/bin/python3 agent_access.py validate; echo "rc=$?"; echo ---; /opt/homebrew/bin/python3 -m unittest discover -s tests 2>&1 | tail -4; echo "rc=$?"
cd <guest-path> && grep -n "add_parser\|add_argument\|--output\|def main\|stdout\|open(" agent_access.py | head -60
cd <guest-path> && sed -n 353,410p agent_access.py
cd <guest-path> && python3 agent_access.py generate | head -60; echo "rc=${PIPESTATUS[0]}"; mkdir -p .coldpass/scoped && cat > .coldpass/scoped/scoped-policy.json <<'EOF'
{
  "version": 1,
  "lan_hosts": [{"name": "printer", "address": "<internal-ip>", "service": "printer"}],
  "agents": [
    {"name": "agent-a", "tag": "tag:agent-agent-a", "preset": "scoped",
     "allow": [{"host": "printer", "ports": ["tcp:631", "udp:8000-8010"]}],
     "never": ["unlisted_lan_hosts","other_agents","internet_or_exit_nodes","tailnet_administration","policy_or_device_changes","all_unlisted_ports"]},
    {"name": "agent-b", "tag": "tag:agent-agent-b", "preset": "everything", "allow": [],
     "never": ["unlisted_lan_hosts","other_agents","internet_or_exit_nodes","tailnet_administration","policy_or_device_changes","all_unlisted_ports"]}
  ]
}
EOF
python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json validate; echo "rc=$?"; python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json summary; echo "rc=$?"
cd <guest-path> && python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json generate | python3 -c 'import json,sys; d=json.load(sys.stdin); print(json.dumps(d["grants"],indent=1)); print(len(d["tests"]),"tests")'; echo "rc=${PIPESTATUS[0]}"; cat > .coldpass/scoped/existing-policy.json <<'EOF'
{"grants": [{"src": ["tag:agent-agent-b"], "dst": ["*"], "ip": ["*"]}]}
EOF
python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json diff --against .coldpass/scoped/existing-policy.json; echo "rc=$?"
cd <guest-path> && sed 's/<internal-ip>/192.0.2.25/' .coldpass/scoped/scoped-policy.json > .coldpass/scoped/placeholder-policy.json && python3 agent_access.py --policy .coldpass/scoped/placeholder-policy.json validate; echo "rc=$?"; python3 agent_access.py --policy .coldpass/scoped/placeholder-policy.json generate; echo "rc=$?"
cd <guest-path> && mkdir -p .coldpass/examples && test ! -e .coldpass/examples/generated-fragment.hujson && python3 agent_access.py generate --output .coldpass/examples/generated-fragment.hujson; echo "rc=$?"; cat .coldpass/examples/generated-fragment.hujson; rm -f .coldpass/examples/generated-fragment.hujson; ls -la .coldpass/examples; python3 agent_access.py --policy .coldpass/scoped/scoped-policy.json summary | tail -5
cd <guest-path> && mkdir -p .coldpass && cat > .coldpass/claims.json <<'EOF'
[
 {"kind":"claim","claim":"scoped mode grants only the listed LAN host and ports","source":"Choose `everything` to grant an agent all IP traffic to all destinations, or `scoped` to grant only its listed LAN hosts and ports.","input":"scoped policy with printer <internal-ip> allowed on tcp:631 for agent-a","expected":"generated grant lists only <internal-ip> with tcp:631 and udp:8000-8010","probe_kind":"cli","argv":["/opt/homebrew/bin/python3","agent_access.py","--policy",".coldpass/scoped/scoped-policy.json","generate"],"stdin":"","expected_text":"<internal-ip>","cwd":"<guest-path>"},
 {"kind":"claim","claim":"a documentation placeholder address is rejected by validation","source":"The address above is a documentation placeholder and is intentionally rejected by validation.","input":"scoped policy using documentation address 192.0.2.25","expected":"validation exits 2 with a private-address policy error","probe_kind":"cli","argv":["/opt/homebrew/bin/python3","agent_access.py","--policy",".coldpass/scoped/placeholder-policy.json","validate"],"expected_returncode":2,"expected_text":"must be a private LAN address within RFC1918 IPv4 ranges","cwd":"<guest-path>"},
 {"kind":"claim","claim":"diff reviews grant changes without writing","source":"To review grant changes without writing, run `python3 agent_access.py diff --against existing-policy.json`;","input":"existing policy with one agent-b grant","expected":"diff prints the agent-a printer grant as an addition and no removals","probe_kind":"cli","argv":["/opt/homebrew/bin/python3","agent_access.py","--policy",".coldpass/scoped/scoped-policy.json","diff","--against",".coldpass/scoped/existing-policy.json"],"expected_text":"+ {\"dst\":[\"<internal-ip>\"]","cwd":"<guest-path>"}
]
EOF
cat > .coldpass/probe.json <<'EOF'
{"kind":"cli","argv":["/opt/homebrew/bin/python3","agent_access.py","--policy",".coldpass/scoped/scoped-policy.json","generate"],"cwd":"<guest-path>","expected_text":"<internal-ip>"}
EOF
cat > .coldpass/examples.json <<'EOF'
[
 {"kind":"example","claim":"quickstart summary lists each agent's grant mode","source":"README.md Quickstart","input":"summary with default policy.json","expected":"summary header and per-agent grant lines","argv":["/opt/homebrew/bin/python3","agent_access.py","summary"],"cwd":"<guest-path>","env":{},"expected_text":"Agent Tailscale grants"},
 {"kind":"example","claim":"validate the default policy","source":"README.md Quickstart","input":"default policy.json","expected":"Policy is valid.","argv":["/opt/homebrew/bin/python3","agent_access.py","validate"],"cwd":"<guest-path>","env":{},"expected_text":"Policy is valid."},
 {"kind":"example","claim":"generate writes the Tailscale policy fragment to a file","source":"README.md Quickstart","input":"generate --output .coldpass/examples/generated-fragment.hujson","expected":"fragment with tagOwners, grants, tests","argv":["/opt/homebrew/bin/python3","agent_access.py","generate","--output",".coldpass/examples/generated-fragment.hujson"],"cwd":"<guest-path>","env":{},"expected_file":".coldpass/examples/generated-fragment.hujson","expected_text":"\"tag:agent-agent-b\""},
 {"kind":"example","claim":"unit test suite (documented in release-check.json)","source":"release-check.json","input":"python3 -m unittest discover -s tests","expected":"35 tests pass","argv":["/opt/homebrew/bin/python3","-m","unittest","discover","-s","tests"],"cwd":"<guest-path>","env":{},"expected_text":"OK"}
]
EOF
cat > .coldpass/cycles.json <<'EOF'
{"detected":false,"reason":"Entry points inspected: agent_access.py main() dispatches one-shot subcommands (validate, generate, summary, diff) and exits; README.md and release-check.json define no cron, scheduler, loop, webhook, --once or --now trigger, and CI workflows contain only a bug-report template. The tool runs once per invocation, so no product cycle exists.","checks":[]}
EOF
for f in claims probe examples cycles; do /opt/homebrew/bin/python3 -I -c "import json,sys; json.load(open('.coldpass/$f.json')); print('$f ok')"; done
cd <guest-path> && COLDPASS_WORKSPACE=<guest-path> /opt/homebrew/bin/python3 -I <guest-path> --validate --replay; echo "rc=$?"
cd <guest-path> && cat > .coldpass/report.json <<'EOF'
{"outcome":"working","fault_owner":null,"operation":"Generate and review Tailscale grant fragments for three agents with the offline agent_access.py CLI (summary, validate, generate, diff), including scoped mode","operation_scope":"Offline only; Python 3.14.8 at /opt/homebrew/bin/python3 (README needs 3.10+); no network, no Tailscale connection, no browser or credentials. Output is a review fragment; nothing is applied to a live tailnet.","steps":["python3 agent_access.py summary","python3 agent_access.py validate","python3 agent_access.py generate --output generated-fragment.hujson","python3 agent_access.py diff --against existing-policy.json","Copy policy.json to policy.local.json and set an agent preset to scoped (done via --policy .coldpass/scoped/scoped-policy.json instead)","python3 -m unittest discover -s tests (from release-check.json; 35 tests OK)"],"deviations":["No git init/fetch of the pinned commit was run: the README commands need no Git metadata, and the snapshot in <guest-path> was used as provided.","Did not create policy.local.json in the checkout; used the documented --policy flag with a scoped example policy in .coldpass/scoped/ (documentation-range and <internal-ip> example addresses; the README says real addresses must stay out of the repo).","Probes use absolute /opt/homebrew/bin/python3 in argv; the generate probe reads stdout instead of writing a file.","The diff claim's existing policy file (.coldpass/scoped/existing-policy.json) is a hand-written sample with one grant, since the repo has no existing Tailscale policy.","Validation negative case uses a placeholder policy file in .coldpass/scoped/ to show the README's documented rejection of 192.0.2.25."],"stuck_step":null,"main_blocker":null,"plain_failure":null,"suggested_fix":null}
EOF
/opt/homebrew/bin/python3 -I -c "import json; json.load(open('.coldpass/report.json')); print('report ok')"; ls -la .coldpass; COLDPASS_WORKSPACE=<guest-path> /opt/homebrew/bin/python3 -I <guest-path> --validate --replay | /opt/homebrew/bin/python3 -I -c "import json,sys; d=json.load(sys.stdin); print('valid', d['valid'], 'problems', d['problems'], 'replay', d['replay']['status'])"
run JSON · checker evidence · agent report + check · transcript excerpt · error excerpt unavailable